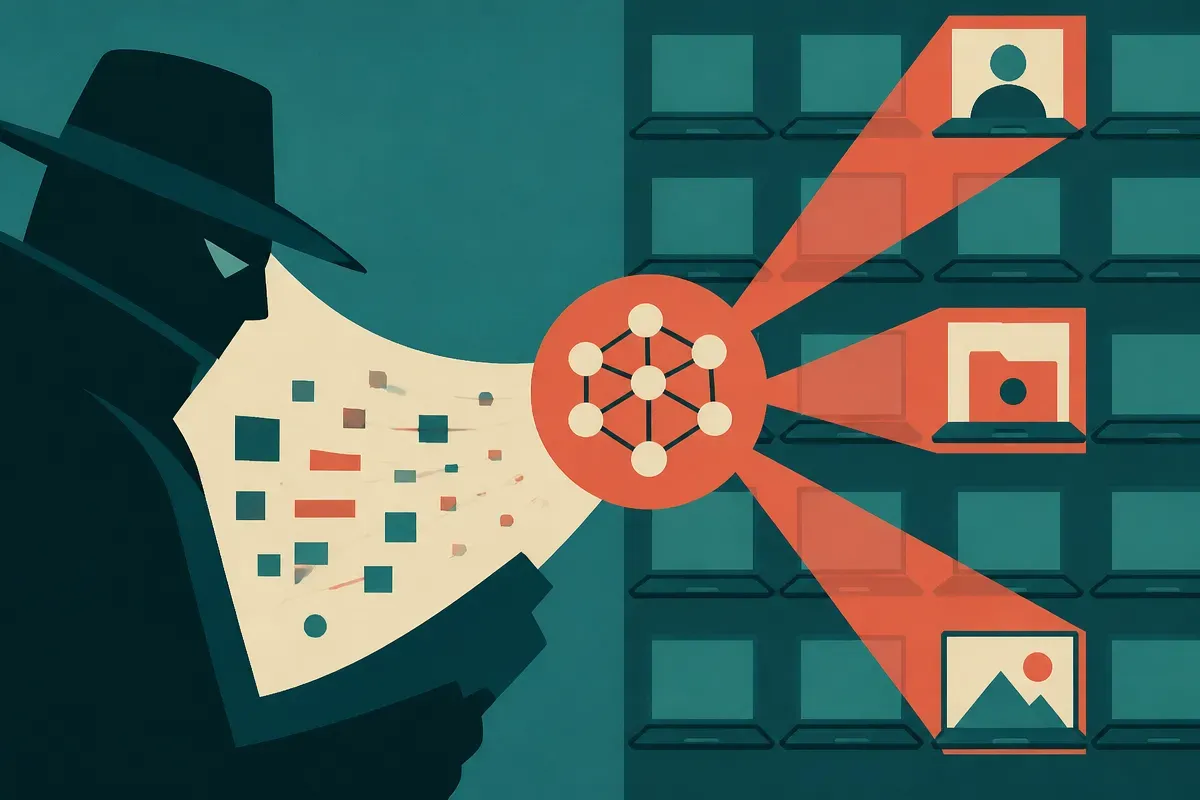
Malware using LLMs for victim triage is the practical AI security problem
A thin but important report points to a likely shift in malware: less magic autonomy, more cheap triage that helps attackers decide which compromised machines deserve time, pressure, and follow-up.
TL;DR: The useful threat model is not “AI malware thinks for itself,” it is malware using LLMs as cheap judgment layers to sort stolen context and prioritize the most valuable victims.
What does “LLM-ranked victims” actually mean?
The primary material here is thin: a Hacker News AI item titled “Malware uses LLMs to rank victims by how much they’re worth.” That is not the same as a named lab report, vendor writeup, or malware reverse-engineering post with hashes, samples, prompts, and infrastructure details.
Still, the claim is plausible enough to take seriously because the mechanism is boring. And boring is usually where the real adoption happens.
An attacker does not need a frontier model to make malware more useful. They need a cheap classifier that can read messy evidence from a compromised machine and answer questions like: is this a home user, a small business owner, an accountant, a lawyer, an IT admin, a founder, or someone with access to payroll, cloud consoles, crypto wallets, customer databases, or procurement systems?
That is an LLM-shaped task. It is not deep reasoning. It is triage across noisy text.
Traditional malware already steals browser data, documents, screenshots, device metadata, and credentials. The new layer is interpretation. Instead of dumping everything into a panel and making a human operator sift through it, the malware pipeline can ask a model to summarize the victim, estimate business relevance, spot high-value keywords, and route the case to the next action.
That does not make the malware intelligent. It makes the attacker’s queue cleaner.
Why is this more dangerous than “AI writes malware”?
The popular story has been AI generating code for attackers. That matters, but it also gets overplayed. Malware operators already have code. They have kits, loaders, marketplaces, stolen credentials, affiliate programs, and years of operational practice.
The bigger shift is AI lowering the cost of attention.
Crime at scale has a filtering problem. Most stolen data is junk. Most infected machines are not worth hands-on work. Most victims cannot pay much, do not have useful access, or are too noisy to pursue. Human time is the expensive part.
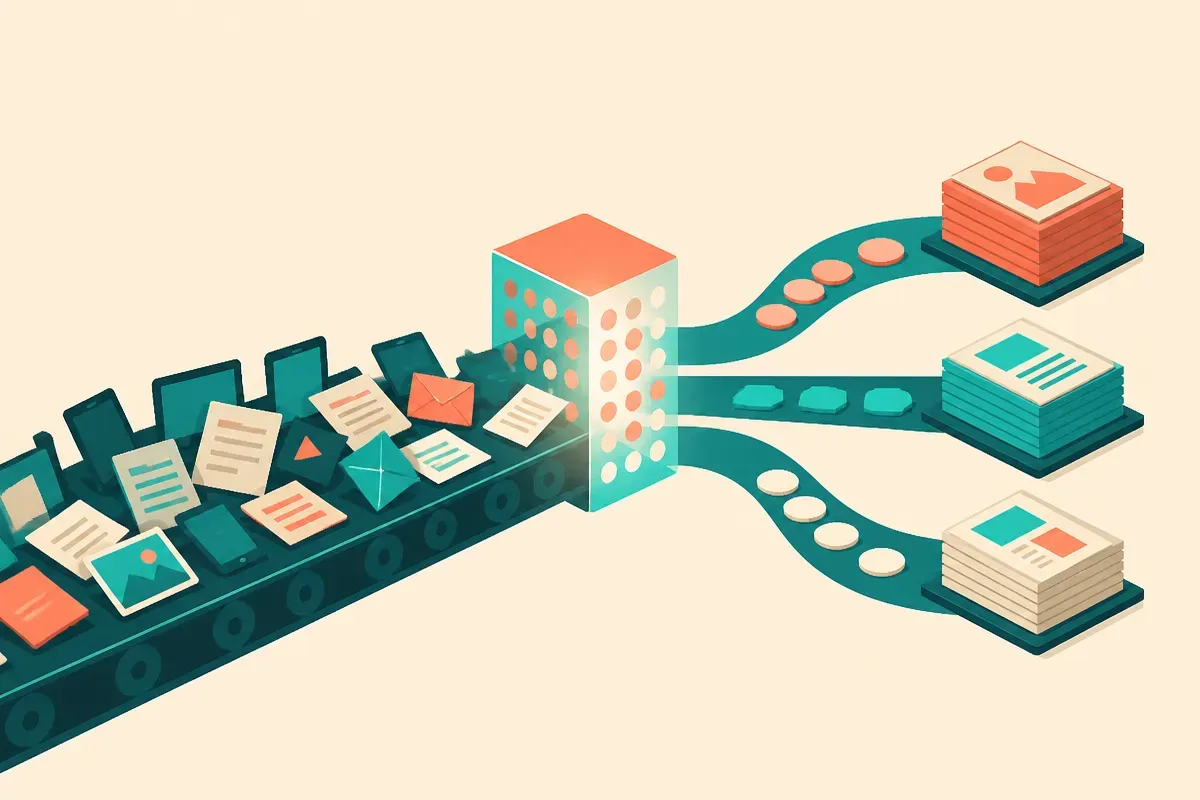
LLMs are good at turning unstructured junk into a short judgment. That changes the economics. A low-skill operator can process more victims. A better operator can spend less time on losers. A ransomware affiliate can decide faster which endpoints look like enterprise beachheads. A credential thief can separate “random shopping login” from “cloud admin account” without reading every artifact.
This is also where defenders should avoid the sci-fi framing. The scary version is not a self-directed agent planning an intrusion from scratch. The near-term version is a set of small model calls inside an existing criminal workflow: classify, summarize, prioritize, draft pressure language, localize the scam, choose the next playbook.
That is enough.
What should defenders change first?
Start by treating local context as the prize, not just credentials. If malware can rank victims by reading their files, browser state, email snippets, screenshots, org charts, invoices, and chat exports, then “what can be inferred from this endpoint?” becomes a security question.
This pushes teams toward better data minimization. Fewer long-lived secrets in browsers. Fewer sensitive exports sitting in Downloads. Less customer data on laptops. Shorter retention for local files. Better separation between personal browsing and work access. Stronger controls around screenshots, clipboard history, synced folders, and unmanaged AI tools that create local caches.
Detection should also look for triage behavior. Not just data exfiltration volume, but staging patterns: small batches of text collected from many locations, compressed summaries, unusual calls to model APIs, repeated file sampling, or local models invoked by suspicious processes. I would not assume attackers always call public APIs. Local inference is getting cheap enough for commodity use in some workflows, especially for classification.
The catch is false confidence. A model ranking “victim value” can be wrong, biased by noisy artifacts, or fooled by decoys. That cuts both ways. Defenders can use canary documents, fake admin breadcrumbs, and monitored high-value-looking files to detect sorting behavior. But those traps need care. A lazy decoy can create noise without catching anything.
Practitioner’s take: if you build or run security for a company, audit one normal employee laptop and ask what an LLM could infer in five minutes from local files, browser data, synced folders, and screenshots. Then remove what does not need to be there, add canaries where they make sense, and watch for small-scale text collection, not just giant data theft. The missed catch is that AI does not need to improve malware execution to improve attacker outcomes. It only needs to improve attacker selection.